Navigating New Federal Data Privacy Regulations 2027: A Business Essential Guide
Anúncios
Decoding the New Federal Data Privacy Regulations: What Businesses Need to Know by 2027
The digital landscape is constantly evolving, and with it, the imperative for robust data protection. Businesses worldwide are grappling with an increasingly complex web of regulations designed to safeguard personal information. In the United States, a significant shift is on the horizon with New Federal Data Privacy Regulations poised to take effect on January 1, 2027. This comprehensive guide will delve into what these regulations entail, their potential impact on your business, and the crucial steps you need to take now to ensure compliance and avoid costly penalties.
Understanding and preparing for these changes is not merely a legal obligation; it’s a strategic imperative. Consumer trust, brand reputation, and operational efficiency are all intrinsically linked to how effectively an organization manages and protects personal data. Ignoring these forthcoming regulations could lead to severe financial repercussions, legal challenges, and irreparable damage to your business’s standing in the market. As we approach the 2027 deadline, proactive engagement with these new standards will distinguish leaders from those who fall behind.
The Genesis of Federal Data Privacy 2027: Why Now?
For years, the U.S. has operated under a patchwork of state-specific data privacy laws, leading to inconsistencies and challenges for businesses operating across state lines. While states like California (CCPA/CPRA), Virginia (VCDPA), and Colorado (CPA) have pioneered comprehensive privacy frameworks, the absence of a unified federal standard has created a fragmented regulatory environment. The Federal Data Privacy 2027 regulations aim to provide a more cohesive and standardized approach to data protection across the nation.
Anúncios
The impetus for these new federal regulations stems from several factors:
- Increasing Data Breaches: The sheer volume and sophistication of cyberattacks have highlighted the vulnerability of personal data, prompting a greater demand for stringent security measures.
- Growing Consumer Awareness: Individuals are becoming increasingly aware of their digital rights and the value of their personal data, leading to calls for greater control and transparency.
- Global Harmonization: The success of international frameworks like the GDPR in Europe has demonstrated the benefits of a comprehensive privacy law, influencing the push for similar standards in the U.S.
- Technological Advancements: The rapid evolution of AI, big data analytics, and IoT devices has created new challenges and opportunities for data collection and processing, necessitating updated regulatory oversight.
These new regulations are not just an expansion of existing laws; they represent a fundamental shift in how businesses must approach data handling, from collection and storage to processing and deletion. The goal is to establish a baseline of protection for all U.S. citizens, fostering trust in the digital economy and holding organizations accountable for their data practices.
Understanding the ‘why’ behind these regulations is crucial for businesses to appreciate their significance and to motivate the necessary internal changes. It’s about more than just compliance; it’s about adapting to a new era where data privacy is a core business value.
Anúncios
Key Provisions and Core Principles of the New Federal Data Privacy 2027 Regulations
While the final specific text of the Federal Data Privacy 2027 regulations is still being meticulously reviewed and finalized, the overarching principles and expected key provisions are becoming clearer. Businesses should begin preparing based on these anticipated elements, as they are likely to form the bedrock of the new legal framework.
1. Expanded Definition of Personal Data
Expect a broad definition of "personal data" that goes beyond traditional identifiers like names and addresses. This will likely include IP addresses, biometric data, geolocation data, online identifiers, and even inferences drawn from data that could identify an individual. This expanded scope means more data types will fall under regulatory protection, requiring businesses to reassess their data inventories.
2. Enhanced Consumer Rights
A cornerstone of modern privacy laws, these regulations will undoubtedly grant consumers stronger rights regarding their data. These typically include:
- Right to Know: The right to be informed about what personal data is being collected, used, shared, or sold.
- Right to Access: The right to request and obtain copies of their personal data held by a business.
- Right to Correct/Rectify: The right to request corrections of inaccurate or incomplete personal data.
- Right to Delete: The right to request the deletion of their personal data, with certain exceptions.
- Right to Opt-Out: The right to opt-out of the sale or sharing of their personal data, particularly for targeted advertising.
- Right to Portability: The right to receive their personal data in a structured, commonly used, and machine-readable format.
Businesses will need robust mechanisms to facilitate these requests efficiently and within specified timeframes.
3. Data Minimization Principles
The regulations are expected to emphasize data minimization, meaning businesses should only collect personal data that is necessary for a specific, stated purpose. This principle encourages organizations to be more intentional about their data collection practices and to avoid hoarding unnecessary information.
4. Purpose Limitation
Data collected for one purpose should not be used for an entirely different, unrelated purpose without explicit consumer consent. This ensures transparency and prevents businesses from repurposing data in ways consumers didn’t anticipate.
5. Data Security Requirements
A critical component will be the mandate for businesses to implement reasonable security measures to protect personal data from unauthorized access, disclosure, alteration, and destruction. While not prescriptive about specific technologies, the regulations will likely require a risk-based approach, taking into account the type of data, the potential harm from a breach, and the state of technological advancements.
6. Accountability and Governance
Businesses will be expected to demonstrate accountability for their data processing activities. This could involve maintaining records of processing activities, conducting Data Protection Impact Assessments (DPIAs) for high-risk processing, and potentially appointing Data Protection Officers (DPOs) for larger organizations. Robust internal policies and training programs will be essential.
7. Consent Requirements
The regulations will likely clarify and strengthen consent requirements, moving towards an "opt-in" model for certain types of data processing, especially for sensitive personal information or the sale/sharing of data. Consent must be freely given, specific, informed, and unambiguous.
8. Data Breach Notification
Clear guidelines for notifying affected individuals and regulatory authorities in the event of a data breach are anticipated. These guidelines will likely include specific timelines and content requirements for notifications.
These provisions, while potentially challenging to implement, are designed to create a more secure and transparent data ecosystem. Proactive planning and investment in compliance will be key to navigating the new landscape of Federal Data Privacy 2027.
Who Will Be Affected by the Federal Data Privacy 2027 Regulations?
The reach of the Federal Data Privacy 2027 regulations is expected to be broad, impacting a vast array of businesses, regardless of size or sector. Unlike some state laws that apply only to businesses meeting certain revenue or data processing thresholds, a federal law could potentially cover almost any entity that collects, processes, or stores personal data of U.S. residents.
Small, Medium, and Large Enterprises
While larger corporations with extensive data operations will undoubtedly face significant compliance burdens, small and medium-sized enterprises (SMEs) should not assume they are exempt. Even a local retail store collecting customer email addresses for a loyalty program or a small online business processing payment information will likely fall under the purview of these regulations. The key differentiator might be the scope of requirements, with some provisions potentially scaled for smaller entities, but the fundamental obligations will remain.
Businesses Across All Sectors
Any industry that handles consumer data will be affected. This includes, but is not limited to:
- Technology Companies: Social media platforms, app developers, cloud service providers, and e-commerce giants.
- Healthcare Providers: Hospitals, clinics, pharmacies, and health tech companies (even beyond HIPAA, which focuses on health information, these regulations will cover broader personal data).
- Financial Institutions: Banks, credit unions, investment firms, and fintech companies.
- Retail and E-commerce: Online and brick-and-mortar stores collecting customer purchase history, contact information, and browsing data.
- Marketing and Advertising Agencies: Companies involved in targeted advertising, data brokerage, and analytics.
- Educational Institutions: Schools, colleges, and universities that collect student and faculty data.
- Service Providers: Any business offering services that require the collection of personal information, from salons to software-as-a-service (SaaS) companies.
The critical factor is whether your business processes personal data of individuals residing in the U.S. If it does, even if your business is based internationally, these regulations will likely apply, similar to the extraterritorial reach of GDPR.
Third-Party Data Processors
Companies that process data on behalf of other businesses (e.g., cloud hosting providers, marketing automation platforms, payroll services) will also have significant obligations. The regulations are expected to impose clear contractual requirements between data controllers (the business collecting the data) and data processors (the business processing it), ensuring a chain of accountability.
It is imperative for every business to conduct a thorough assessment of its data processing activities to determine the extent of its obligations under the Federal Data Privacy 2027 regulations. Ignorance of the law is not a defense, and proactive preparation is the only way to safeguard your organization.
Preparing for Federal Data Privacy 2027: A Strategic Roadmap
The January 1, 2027 deadline may seem distant, but the scope of work required for compliance with Federal Data Privacy 2027 is substantial. Proactive planning and a phased approach are essential. Here’s a strategic roadmap to guide your preparation:
Phase 1: Discovery and Assessment (Now – Early 2025)
- Data Inventory and Mapping:
- Identify all personal data: What personal data do you collect? Where is it stored? How is it transmitted? Who has access to it?
- Map data flows: Document the entire lifecycle of personal data within your organization, from collection to deletion.
- Categorize data: Distinguish between general personal data and sensitive personal data (e.g., health information, financial data, biometric data), as these may have different requirements.
- Gap Analysis:
- Compare your current data handling practices, privacy policies, and security measures against the anticipated requirements of the Federal Data Privacy 2027 regulations.
- Identify areas of non-compliance or significant gaps that need addressing.
- Stakeholder Identification:
- Determine key internal stakeholders (IT, legal, marketing, HR, product development) who will be responsible for implementing changes.
- Consider engaging external legal counsel or privacy consultants specializing in U.S. data privacy law.
Phase 2: Policy and Process Development (Mid 2025 – Early 2026)
- Update Privacy Policies and Notices:
- Revise your public-facing privacy policies to clearly inform consumers about data collection, usage, sharing, and their rights under the new regulations.
- Ensure transparency and use clear, concise language.
- Establish Data Subject Request (DSR) Procedures:
- Develop robust processes for handling consumer requests (access, deletion, correction, opt-out, etc.).
- Define timelines for responding to requests and mechanisms for verifying the identity of the requester.
- Review and Update Vendor Contracts:
- Assess all third-party vendors and service providers who process personal data on your behalf.
- Ensure contracts include data protection clauses that align with the new federal regulations, assigning clear responsibilities and liabilities.
- Implement Data Protection Impact Assessments (DPIAs):
- Establish a process for conducting DPIAs for new projects, technologies, or processing activities that involve high risks to data privacy.
- Strengthen Consent Mechanisms:
- Audit and update all consent forms and mechanisms to ensure they meet the new "freely given, specific, informed, and unambiguous" standards, especially for sensitive data or marketing.
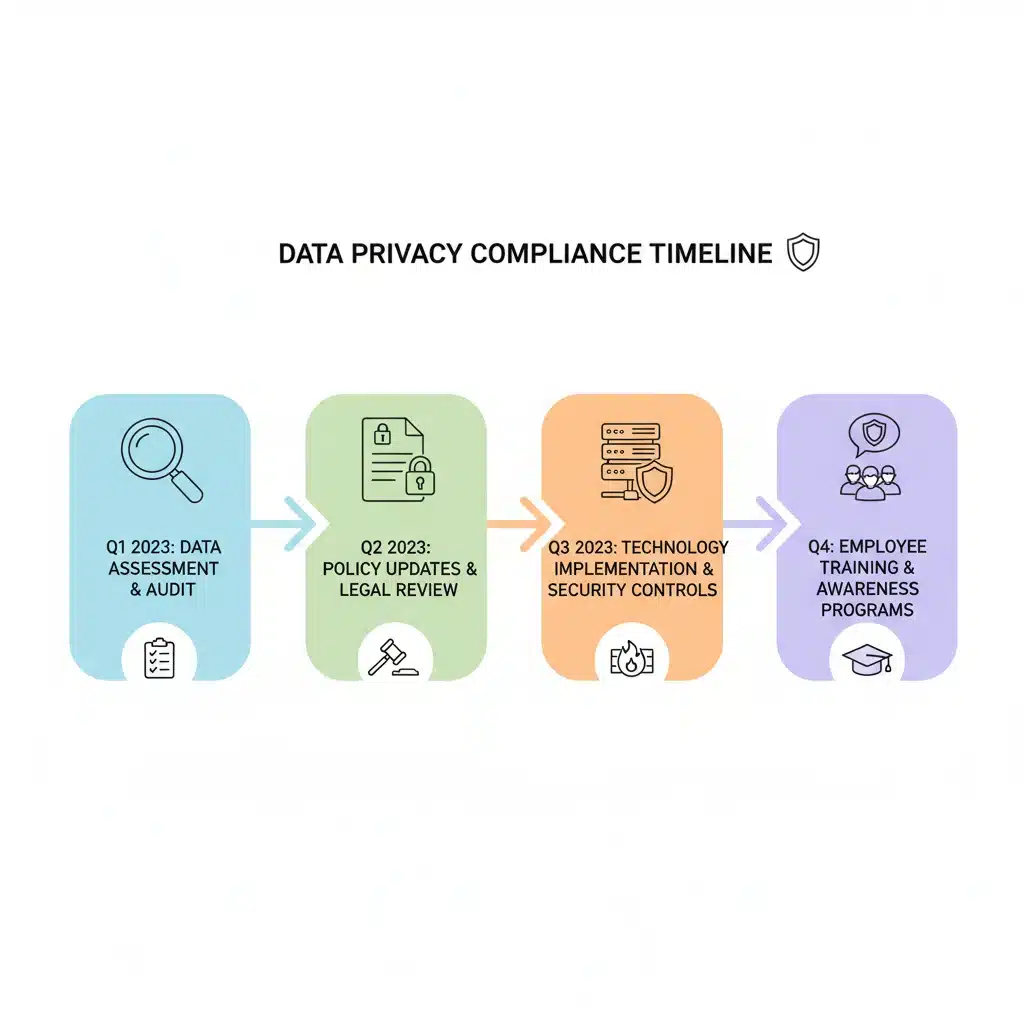
Phase 3: Technology and Security Implementation (Mid 2026 – End 2026)
- Enhance Data Security:
- Implement or upgrade technical and organizational security measures (e.g., encryption, access controls, pseudonymization, regular security audits) to protect personal data.
- Develop and test a comprehensive data breach response plan.
- Data Governance Tools:
- Consider investing in data governance platforms that can help automate data mapping, consent management, DSR fulfillment, and compliance reporting.
- Privacy-by-Design and Default:
- Integrate privacy considerations into the design and development of all new systems, products, and services from the outset.
- Ensure that the strictest privacy settings are the default, requiring users to actively opt-in for less private options.
- Data Retention and Deletion Policies:
- Formalize and implement data retention schedules based on legal requirements and business necessity.
- Establish secure data deletion processes to ensure data is permanently removed when no longer needed or requested by a data subject.
Phase 4: Training and Continuous Compliance (Ongoing)
- Employee Training:
- Conduct mandatory and regular training for all employees who handle personal data.
- Educate them on the new regulations, your updated policies, and their role in maintaining data privacy and security.
- Internal Audits and Monitoring:
- Regularly audit your compliance practices to ensure ongoing adherence to the Federal Data Privacy 2027 regulations.
- Monitor regulatory updates and adjust your compliance program as needed.
- Accountability and Documentation:
- Maintain comprehensive records of your data processing activities, consent records, DSR responses, and compliance efforts. This documentation will be crucial in demonstrating compliance to regulators.
This roadmap provides a structured approach, but flexibility is key. Businesses should stay informed about the final legislative details and adapt their strategies accordingly. The investment now will pay dividends in reduced risk, enhanced trust, and sustained business operations post-2027.
The Ramifications of Non-Compliance: Penalties and Reputational Damage
The stakes for complying with the Federal Data Privacy 2027 regulations are incredibly high. Non-compliance will likely result in severe penalties, both financial and reputational, which could significantly impact a business’s long-term viability and market position.
Financial Penalties
While the exact figures are yet to be finalized, federal privacy laws typically carry substantial fines, often structured in ways that can quickly escalate. These could include:
- Per-Violation Fines: A set amount for each instance of non-compliance, which can multiply rapidly depending on the number of affected individuals or data records.
- Percentage of Annual Revenue: Similar to GDPR, fines might be calculated as a percentage of a company’s global annual turnover, which can amount to billions for large corporations.
- Tiered Penalties: Different levels of fines for minor infractions versus egregious violations, with higher penalties for intentional disregard of the law or repeated offenses.
- Civil Litigation: The new regulations may also include a private right of action, allowing individuals to sue businesses directly for privacy violations, leading to significant legal fees, settlements, and damages.
These financial burdens can cripple small businesses and significantly impact the bottom line of larger enterprises, diverting resources from innovation and growth.
Reputational Damage and Loss of Trust
Beyond monetary fines, the damage to a business’s reputation can be far more enduring and detrimental. A privacy violation or data breach can lead to:
- Erosion of Customer Trust: Consumers are increasingly sensitive to how their data is handled. A breach of trust can lead to customer churn, boycotts, and a reluctance to engage with your brand.
- Negative Public Perception: Media coverage of privacy failures can tarnish a company’s image, making it difficult to attract new customers, partners, or even talent.
- Competitive Disadvantage: Businesses with a strong privacy posture will gain a competitive edge, as consumers and partners increasingly prioritize data protection. Those with a poor record will struggle to compete.
- Investor Scrutiny: Investors are increasingly factoring ESG (Environmental, Social, and Governance) considerations into their decisions, and data privacy is a significant "G" factor. Non-compliance could deter investment.
- Regulatory Scrutiny: A history of non-compliance or data breaches can lead to increased oversight and more frequent audits from regulatory bodies.
The long-term effects of a damaged reputation can far outweigh the immediate financial penalties, impacting brand value, market share, and employee morale. Therefore, viewing compliance with Federal Data Privacy 2027 as an investment in trust and sustainability, rather than just a cost, is crucial.
Leveraging Federal Data Privacy 2027 for Business Advantage
While the prospect of new regulations can seem daunting, the Federal Data Privacy 2027 framework presents an opportunity for businesses to gain a competitive edge and build stronger relationships with their customers. Rather than viewing compliance solely as a burden, forward-thinking organizations can leverage these changes for strategic advantage.
1. Building and Reinforcing Customer Trust
In an era of increasing data breaches and privacy concerns, businesses that demonstrate a clear commitment to protecting personal data will stand out. Transparent privacy practices, adherence to consumer rights, and robust security measures can significantly enhance customer trust and loyalty. This trust translates into repeat business, positive word-of-mouth, and a stronger brand reputation.
2. Streamlining Data Management and Operations
The process of conducting a data inventory and mapping data flows for compliance purposes forces organizations to gain a deeper understanding of their data assets. This can lead to:
- Improved Data Quality: By identifying and addressing inaccuracies or redundancies, businesses can improve the overall quality of their data.
- Reduced Data Clutter: Data minimization principles encourage the deletion of unnecessary data, reducing storage costs and simplifying data management.
- Enhanced Operational Efficiency: Clear data governance policies and automated processes for handling data subject requests can streamline operations and reduce manual effort.
3. Fostering Innovation with Privacy-by-Design
Integrating privacy considerations from the outset of product and service development (privacy-by-design) can lead to more innovative and user-centric solutions. Products built with privacy in mind are often more secure, transparent, and resilient, which can be a significant differentiator in the market. This approach can also reduce the need for costly retrofitting of privacy features later on.
4. Strengthening Cybersecurity Posture
The enhanced data security requirements of the Federal Data Privacy 2027 regulations will compel businesses to strengthen their cybersecurity defenses. This proactive investment not only helps meet compliance obligations but also provides better protection against cyber threats, reducing the risk of costly data breaches and associated downtime. A strong security posture is a foundational element of business resilience.
5. Facilitating International Business
A unified federal privacy law in the U.S. could simplify compliance for international businesses operating in the country. Furthermore, a robust federal framework that aligns with global standards (like GDPR) can facilitate cross-border data transfers and partnerships, making U.S. businesses more attractive to international collaborators.
6. Gaining a Competitive Edge
Businesses that embrace compliance early and effectively will differentiate themselves from competitors who lag. Being able to confidently assure customers, partners, and regulators of your commitment to data privacy can be a powerful marketing tool and a significant competitive advantage in a privacy-conscious market.
By approaching the Federal Data Privacy 2027 regulations with a strategic mindset, businesses can transform a regulatory challenge into an opportunity for growth, innovation, and enhanced customer relationships.
Looking Ahead: The Evolving Landscape of Data Privacy
The implementation of the Federal Data Privacy 2027 regulations marks a pivotal moment in the history of data protection in the United States. However, it is crucial for businesses to recognize that data privacy is not a static field; it is an ever-evolving landscape influenced by technological advancements, shifting consumer expectations, and global regulatory trends.
Continuous Monitoring and Adaptation
Compliance cannot be a one-time project. Businesses must establish internal mechanisms for continuous monitoring of their data processing activities and stay abreast of any amendments or supplementary regulations that may emerge. The digital world moves fast, and what is compliant today might require adjustments tomorrow. Regular internal audits, privacy impact assessments for new initiatives, and ongoing employee training will be essential components of a sustainable compliance program.
The Role of Emerging Technologies
Technologies like Artificial Intelligence (AI), Machine Learning (ML), and the Internet of Things (IoT) are rapidly changing how data is collected, processed, and analyzed. Future iterations of data privacy regulations will likely address specific concerns related to these technologies, such as algorithmic bias, facial recognition data, and the privacy implications of connected devices. Businesses that are proactive in integrating privacy-by-design principles into their AI and IoT strategies will be better positioned for future regulatory shifts.
Global Interoperability
As businesses increasingly operate on a global scale, the desire for greater interoperability between different national and international privacy frameworks will grow. While the Federal Data Privacy 2027 regulations will provide a unified U.S. standard, businesses with international operations will still need to navigate the complexities of GDPR, various Asian privacy laws, and other regional regulations. The development of global privacy standards or mechanisms for easier cross-border compliance remains a long-term goal.
Consumer Expectations as a Driving Force
Beyond legal mandates, consumer expectations will continue to be a powerful force shaping data privacy practices. Individuals are becoming more informed and empowered, demanding greater transparency, control, and accountability from organizations that handle their data. Businesses that excel in meeting these expectations, even beyond the letter of the law, will foster deeper trust and loyalty, which are invaluable assets in today’s competitive market.
The journey towards comprehensive data privacy compliance with Federal Data Privacy 2027 is a significant undertaking, but it is also an ongoing commitment. By embedding privacy into the core of their business operations and maintaining a forward-looking perspective, organizations can not only meet their legal obligations but also thrive in an increasingly data-conscious world.
Conclusion: Proactive Steps for a Compliant Future
The advent of the New Federal Data Privacy Regulations on January 1, 2027, marks a new era for businesses operating within the United States. This federal mandate is not merely another regulatory hurdle but a fundamental shift in how organizations must approach the collection, processing, and protection of personal data. The fragmented landscape of state-specific laws will give way to a more unified, albeit stringent, framework designed to empower consumers and hold businesses accountable.
For every business, regardless of size or industry, the message is clear: procrastination is not an option. The time between now and the 2027 deadline is essential for conducting thorough data inventories, reassessing current practices, and implementing robust compliance programs. This involves:
- Understanding the Core Provisions: Familiarize yourself with the expanded definition of personal data, enhanced consumer rights, data minimization principles, and stringent security requirements.
- Conducting a Comprehensive Assessment: Map your data flows, identify gaps in your current privacy posture, and determine the full extent of your obligations.
- Developing and Updating Policies: Revise privacy notices, establish clear procedures for data subject requests, and update vendor contracts to reflect the new federal standards.
- Investing in Technology and Security: Implement necessary technical and organizational measures to protect data, including encryption, access controls, and a robust data breach response plan.
- Prioritizing Training and Accountability: Educate all employees on the new regulations and their responsibilities, and maintain thorough documentation of all compliance efforts.
The consequences of non-compliance extend far beyond financial penalties; they encompass significant reputational damage, loss of customer trust, and potential long-term harm to your brand and market position. Conversely, businesses that proactively embrace these regulations can transform them into a strategic advantage, fostering deeper customer relationships, streamlining operations, and building a more resilient and trustworthy organization.
The journey to full compliance with Federal Data Privacy 2027 is complex and continuous. It requires a dedicated commitment from leadership, cross-functional collaboration, and a willingness to adapt to an evolving regulatory environment. By taking decisive action now, businesses can not only meet their legal obligations but also position themselves for sustained success in a future where data privacy is paramount.
Begin your preparation today to ensure your business is not just compliant, but thriving, in the new era of federal data privacy.